Surreal glass vault of regulatory data and dissolving documents

Regvra

The compliance operating system for firms that can’t afford blind spots.

A customizable platform for mid-sized and large financial institutions — regulatory intelligence, investment monitoring, surveillance, reporting, and investigations — with explainable AI. Rules decide. Humans approve.

Scroll the story

The idea

Not another portal. A configurable regulatory nervous system for your firm.

One customizable package for mid-sized and large firms: turn on the modules you need, encode your policies, connect your data, and keep an audit trail regulators can trust.

Problems

  • Excel / PDF mandates and late breach discovery
  • Vendor sprawl and incomplete data
  • Alert noise without clear explanations
  • Regulatory change with no owners or deadlines

What Regvra does

  • Codify rules and monitor holdings continuously
  • Gate data quality before detection
  • Explain alerts; humans approve actions
  • Export evidence packs for audit and regulators
app.regvra.com/overview

LIVE · REGVRA

Firm-wide compliance desk

All entitiesT-1 EODUK + EUExport
Rules live1,284+18
Pass rate94.2%+1.1%
Near-breach27+4
Open breaches3−1
DQ gate99.1%stable
SLA risk2critical
Alert volume vs false-positive rate
Alerts FP% Auto-closed
30dW-3W-2W-1Today
Jurisdiction heat
UKEUUSAPAC
Control health
Pre-trade
Post-trade
Comms
Priority queue · cross-module● streaming
TimeEntityModuleSignalSeverityOwner
08:14:02ACME GlobalInvestmentSector tech 27.1%BreachL2 · Maya
08:11:40ACME CreditDisclosure13D aggregationNearL1 · Raj
08:09:18Desk EQ-EUTrade surv.Layering score 0.81HighL2 · Ana
08:07:55ACME MultiCommsOff-channel lexiconMedL1 · Tom
08:04:12HoldCo APACReg changeFCA MW-81 mappedInfoPolicy
ProblemExcel mandates

Rules trapped in sheets and PDFs.
ProblemVendor sprawl

Too many tools, one incomplete picture.
ProblemAlert fatigue

Noise hides the real risk.

ProblemChange overload

New rules, no clear owners.

SolutionDeterministic rules

Thresholds you can defend in audit.

SolutionExplainable AI

Why it fired — with sources.

SolutionEvidence packs

Ready when regulators ask.

SolutionOne workspace

Alerts, tasks, and cases together.

ProblemExcel mandates

Rules trapped in sheets and PDFs.

ProblemVendor sprawl

Too many tools, one incomplete picture.

ProblemAlert fatigue

Noise hides the real risk.

ProblemChange overload

New rules, no clear owners.

SolutionDeterministic rules

Thresholds you can defend in audit.

SolutionExplainable AI

Why it fired — with sources.

SolutionEvidence packs

Ready when regulators ask.

SolutionOne workspace

Alerts, tasks, and cases together.

Step-by-step

How the story clicks — before you ever book a call

Scroll these six moves. By the last one, you should already know whether Regvra is the system you’d demo next week.

Step 01

See the real pain clearly

Excel mandates, alert fatigue, disclosure complexity, and vendor sprawl aren’t “nice to automate” — they’re where breaches, fines, and wasted analyst hours hide.
  • Mid-sized: spreadsheet & staffing limits
  • Large: data quality, aggregation, multi-vendor noise
Mandate and spreadsheet pain atmosphere
Step 02

Encode your firm — not a generic checklist

Regvra starts from your entities, funds, policies, and workflows. The platform is the skeleton; your rule packs and approvals make it yours.
  • Guideline studio: clause → rule → test
  • Workflow severities, owners, and SLAs
Modular customization wall
Step 03

Connect data with a quality gate

CSV, SFTP, or APIs land behind completeness and lineage checks. Bad data becomes a visible issue — not a silent surveillance blind spot.
  • Upstream DQ before alerts
  • Quarantine + lineage for audit
Data quality gate filtering corrupted streams
Step 04

Detect with deterministic rules

Mandates, thresholds, and scenarios fire with a calculation trail. You can defend every breach call in an audit room.
  • Near-breach warnings
  • Versioned rules & evidence packs
Mechanical rules engine macro
Step 05

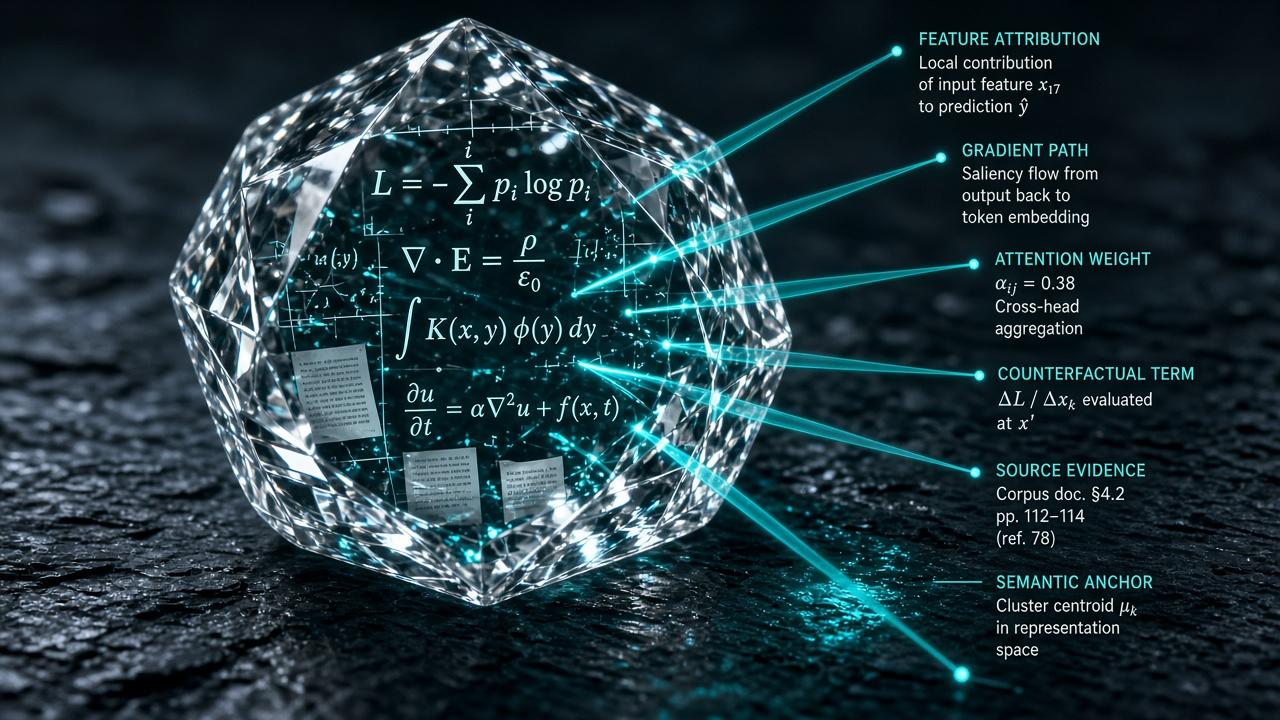
Let AI explain — humans decide

AI drafts the why, clusters noise, and prepares investigation notes with citations. It never silently files or closes something consequential.
  • Explain every alert
  • Draft memos with sources
  • Approval gate always on
Explainable AI crystal with citation beams
Step 06

Walk out with a scoped first win

By the time you reach a demo, you already know the path: pilot monitoring + reg intel, or enterprise suite depth — same platform, different packing.
  • 14–30 day paid pilot for mid-market
  • Enterprise path: connectors, ABAC, private deploy
Ascending path of platforms toward clarity
The moment a compliance leader chooses the demo path

Feeling it?

If those six steps match your week — the demo is the next logical move.

Bring one ugly mandate spreadsheet or one noisy alert queue. We’ll map it to a scoped pilot or an enterprise walkthrough — not a generic feature tour.

Current industry pain

What firms are actually fighting

Research across buy-side and sell-side points to the same structural failures: fragmented controls, weak data, noisy alerts, and change overload — amplified at enterprise scale by cross-border disclosure and multi-vendor stacks.

Excel & fragmented mandates

Rules live in PDFs, OMS notes, and spreadsheets. Breaches surface late. Audit trails are reconstructed after the fact.

Mid + Large

Guideline coding drift

IMA language is ambiguous. Coded rules diverge from source documents. Few firms reconcile systematically.

Mid + Large

Data quality & volume

Surveillance fails upstream. Incomplete venues, bad timestamps, and siloed feeds create both noise and blind spots.

Especially Large

Alert fatigue

False positives consume analyst hours. Real risk hides in the pile. Teams need explainability, not more raw alerts.

Mid + Large

Regulatory change overload

New obligations arrive faster than headcount. Boards still expect delivery — even during cost cuts.

Mid + Large

Cross-border disclosure complexity

Aggregation across funds, entities, and instruments differs by jurisdiction. Manual country-by-country processes break.

Large buy-side

Vendor sprawl & legacy lock-in

Multiple surveillance and monitoring tools don’t share a data plane. Integration cost exceeds license cost.

Large

Untrusted black-box AI

Firms want AI assistance — but regulators and policies demand citations, auditability, and human approval.

All segments
Macro of a brass and obsidian mechanical rules engine

Deterministic core

A rules engine you can defend in an audit room

Thresholds, mandates, and disclosure calculations are versioned, testable, and explainable. Every alert shows the rule, the inputs, the numbers, and the timestamp. AI never silently “decides” a breach.

  • Guideline studioMap IMA / policy clauses → coded rules → test cases → periodic reconcile against source documents.
  • Near-breach intelligenceCatch drift before it becomes a filing event or board incident.
  • Evidence packsOne export for internal audit, regulators, or client queries — system generated, not rebuilt from email.
Regulatory publication exploding into a constellation of obligations linked to funds

Regulatory change + disclosure

From publication to obligation to action

Horizon-scan regulatory updates, assess impact on your products and entities, and drive tasks with owners and deadlines. For large managers, layer cross-border shareholding aggregation and jurisdiction-specific thresholds on the same data plane.

  • Impact hypotheses with sourcesEvery suggested impact cites the original publication. Compliance approves interpretation.
  • Aggregation across structuresFunds, entities, and instruments rolled into the view each regime actually requires.
  • Executive MIBoard-readable status on change delivery, breaches, coverage, and reporting data quality.
Corrupted data shards filtered through a luminous teal quality gate

Data quality gateway

Stop garbage before it becomes false comfort

Incomplete venues, broken timestamps, and siloed feeds are the real surveillance killers. Regvra puts completeness, lineage, and quarantine upstream of alerts — so detection runs on data you can defend.

  • DQ gates before detectionFlag missing fields, late files, and coverage gaps as first-class issues — not silent blind spots.
  • Lineage you can showTrace a record from source system to alert to case evidence.
  • CSV today, connectors tomorrowStart with a gateway mid-market firms can use; expand connectors for enterprise without rebuilding the core.

Complete suite · modular buy

Customize the package. Keep one operating system.

Drag / scroll horizontally →

01

Regulatory intelligence

Track publications, map obligations to your entities, assign owners and deadlines, and keep every interpretation linked to source.

  • Horizon scan
  • Impact tasks
  • Board-ready MI
02

Investment monitoring

Codify mandates and restrictions. Catch breaches and near-breaches with a full calculation trail — not a spreadsheet tab.

  • Rule packs
  • Near-breach alerts
  • Evidence export
03

Disclosure & positions

Aggregate exposure across funds and entities. Apply jurisdiction thresholds. Know when disclosure obligations arise.

  • Cross-entity view
  • Threshold engine
  • Filing evidence
04

Trade surveillance

Focused market-abuse scenarios with explainable scores — spoofing, layering, wash, front-running — tuned to your desk risk.

  • Scenario packs
  • Model versions
  • Case linkage
05

Comms & archive

Capture, retain, search, and review regulated communications. Build cases that connect messages to trades.

  • Channel coverage
  • Lexicon + NLP
  • Legal hold
06

Reporting & cases

Validate submissions, quarantine bad data, reconstruct activity, and close investigations with an immutable audit trail.
  • TR validation
  • Reconstruction
  • L1→L3 workflow
Glass neural core dissolving into layered citation ledgers

Explainable AI layer

AI that earns trust — or it doesn’t ship

Regvra uses AI to explain alerts, cluster noise, draft investigation notes, and answer natural-language questions across obligations and cases. Every claim can be traced. Consequential actions stay behind human approval.

  • Why this alert?Plain-language causation tied to the rule, the records, and the score factors.
  • Draft, don’t fileInvestigation memos and change summaries prepared for review — never silent auto-submission to regulators.
  • Governed assist levelsMid-market teams get speed. Enterprises get policy controls, audit logs, and model-change history.

AI in depth

Explain. Investigate. Cite. Approve.

Three visual truths of the Regvra AI layer: crystal-clear explanations, investigation assistance across records, and a human gate on every consequential action.
Crystal core refracting citation beams onto exact evidence points
Explainable coreEvery AI statement can pin back to a source fragment, rule, or record — not a black-box vibes score.
Glass-pane AI investigator stitching citation threads across alerts
Investigation assistCluster noise, draft case notes, and assemble context across trades and communications.
Jurisdiction spiral representing governed multi-regime AI policy
Human approval gateSuggest and accelerate — never silently file, disclose, or close without a person.
Evidence vault archive opening into holographic trade and message timelines

Evidence & cases

When the regulator asks, you already have the pack

Cases link alerts, holdings, communications, and decisions into one reconstructable story. Retention, legal hold, and export are first-class — not an afterthought spreadsheet.

  • Immutable audit trailWho saw what, what changed, what was approved — timestamped.
  • One-click evidence packsBuilt for internal audit, clients, and supervisory requests.
  • L1 → L3 workflowClear escalation, SLAs, and ownership for mid and large teams.

Customizable package

Your rules. Your modules. Your deploy.

Massive modular control wall of interchangeable compliance panels
Modular control wall
Architectural modular glass panels suggesting enterprise configuration
Policy & workflow knobs
Glass compliance war room as the unified workspace metaphor
One workspace surface
City mapped as a glowing nervous system of risk pathways

Firm-wide nervous system

Alerts, obligations, evidence, and decisions in one place

Stop hopping portals. Regvra becomes the operating surface for compliance, risk, and ops — connecting desks, entities, and jurisdictions into one visible risk map you can act on.

  • Trade ↔ communications linkageBuild holistic cases when both modules are enabled — without forcing a big-bang cutover.
  • Data quality gatesCompleteness and lineage checks sit upstream of detection so garbage doesn’t become false comfort.
  • Deploy your wayMulti-tenant SaaS for speed, or dedicated / VPC / private for enterprise control and residency.
Mandate monitoring atmosphere for mid-sized asset managers

Mid-sized firms

Replace the spreadsheet era

Live in days with CSV/SFTP. Encode your mandates. Get explainable alerts and evidence packs without a nine-month integration programme.
  • Growth pack: RI + IM + AI + cases
  • 14–30 day paid pilot path
  • Transparent modular pricing
Dramatic surveillance investigation atmosphere

Large / enterprise

Consolidate without chaos

Multi-entity ABAC, disclosure engines, surveillance depth, reporting validation, SSO/SCIM, model-risk evidence, and private deployment — on the same platform mid-market starts on.

  • Enterprise suite + ENT controls
  • Connector programme by priority
  • Coexist with legacy, then replace

Built the way regulated buyers evaluate vendors

Surreal storytelling sells the vision. This section is the sober part: what you see on a demo, how a pilot works, how we handle data, and what we will never fake. We respond within 1 business day.
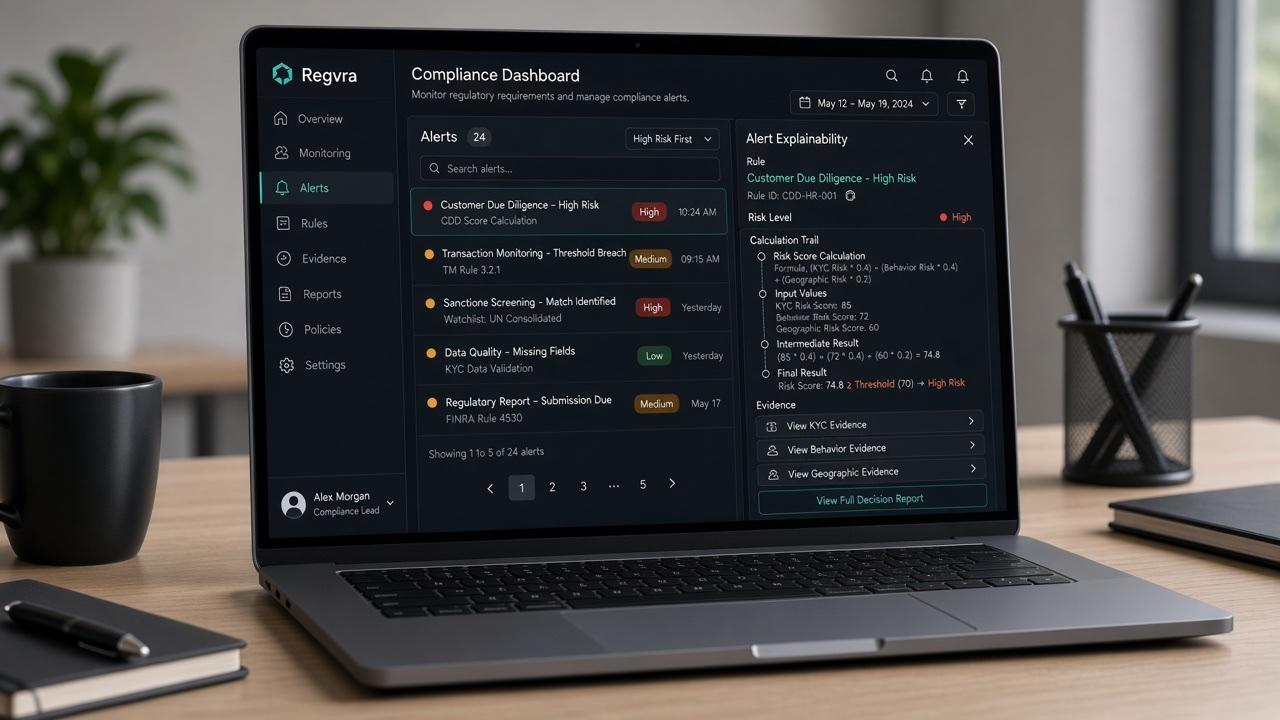
Regvra product interface showing alerts with explanation and evidence trail

What you’ll see on the demo

  • Your-style mandate / obligation example encoded as rules
  • Alert with calculation trail + plain-English explanation
  • Evidence pack export path
  • AI draft note with citations — then human approve
  • Mid Growth vs Enterprise packaging options

Demo format

45-minute scoped walkthrough. No 40-slide fluff. Bring one painful process (Excel mandate sheet or noisy alert queue) and we map it live.

Who we serve

Mid-sized and large asset managers, hedge funds, brokers, and financial institutions that need monitoring, change intelligence, surveillance depth, and audit-ready evidence — without black-box decisions.

Operating principles

Deterministic rules decide thresholds. AI explains, summarises, and drafts. Humans approve consequential actions. Every material output should be reconstructable.

Engagement model

Start with a scoped paid pilot (14–30 day paid pilot), then expand modules. Enterprise deals include security review support, deployment options, and a connector plan — not a surprise SI trap.
Paid pilot — what “yes” buys

  1. Scope workshop: entities, 10–25 rules, data path (CSV/SFTP/API)
  2. Environment stood up with your sample portfolios / obligations
  3. Daily or overnight monitoring run + explainable alerts
  4. Evidence pack + weekly readout with your compliance owner
  5. Go / no-go on Growth or Enterprise packaging with clear pricing

Commercial clarity

  • Pilot: typically $1k–$5k for 14–30 days
  • Growth (mid): ~$1k–$3k / month core pack
  • Professional: ~$3k–$8k / month with added module
  • Enterprise: custom ARR + implementation SOW
  • No lock-in theatre: you keep exported evidence and rule definitions from the pilot
Institutional security operations environment

Security & control posture

Designed for financial-services data handling from day one. We state what is true now and what is on the enterprise roadmap — we do not invent certificates we don’t hold.

  • Tenant isolationLogical separation of customer data; enterprise options for dedicated / VPC / private deploy.
  • Encryption & accessTLS in transit, encryption at rest, least-privilege roles, SSO/SCIM on enterprise path.
  • AuditabilityImmutable activity trail for alerts, approvals, exports, and configuration changes.
  • Residency & retentionRegional deployment options and retention / legal-hold controls for enterprise deals.
  • Assurance roadmapSOC 2 / ISO 27001 path aligned to enterprise procurement — shared honestly during security review, not claimed on the homepage without evidence.
Trust rule we won’t breakWe won’t put fake client logos, fake certifications, or fake case studies on this site. When we earn pilots and attestations, they’ll appear here with real names and permission. Until then: clear product rules, clear pilot scope, clear security design, and a real human response.

Do we have to rip out our current stack?

No. Pilots start beside Excel/OMS exports. Enterprises can coexist with legacy tools, then consolidate module by module.

Will AI make regulatory decisions?

No. AI explains and drafts. Deterministic rules compute breaches. Your team approves consequential actions.

Can large firms do a security review first?

Yes. Enterprise demos include architecture, data-flow, and questionnaire support before production data moves.

What if the pilot doesn’t help?

You leave with exported evidence, rule definitions, and a written readout. We’d rather lose a forced upsell than burn trust.
Refined institutional lounge for demo conversations

Demo & contact

Book a scoped demo — with security questions welcome.

We respond within 1 business day. Tell us your firm, segment, and the first problem to solve. We’ll come back with a 45-minute scoped walkthrough plan or a 14–30 day paid pilot outline — including architecture notes for enterprise reviewers.

Or email hello@regvra.com
We respond within 1 business day. Work email preferred. We don’t sell your details.